Zara Hansen · 3 October 2026
Examining Encryption Protocols That Safeguard Shared Notes in Specialized Digital Platforms
Specialized digital platforms that handle collaborative note-taking rely on layered encryption protocols to protect data during storage and transmission, and these systems integrate standards such as AES-256 for symmetric encryption alongside RSA or ECC for asymmetric key exchanges while maintaining access controls that prevent unauthorized reads even when multiple users edit the same document simultaneously.
Core Protocols in Use
Platforms implement end-to-end encryption models derived from established cryptographic suites where the Signal Protocol extensions provide forward secrecy for shared sessions and TLS 1.3 secures all network communications between clients and servers with perfect forward secrecy built into the handshake process, and researchers at various institutions have documented how these combinations reduce exposure windows during real-time synchronization of notes across devices.
Data from implementations show that zero-knowledge architectures further limit server-side access so that platform operators cannot decrypt content even under legal requests because private keys remain solely with end users who generate them locally before distributing encrypted shares through secure channels.
Key Management Practices
Key derivation functions such as PBKDF2 or Argon2 handle password-based access while hardware security modules store master keys in enterprise deployments and automated rotation schedules update session keys at fixed intervals to limit the impact of any single compromise, and observers note that this approach aligns with guidelines issued by the National Institute of Standards and Technology on cryptographic key management.
Specialized platforms often add attribute-based encryption layers that tie decryption rights to user roles or device attributes so that shared notes remain accessible only to verified collaborators without exposing the full key material during handoff processes.
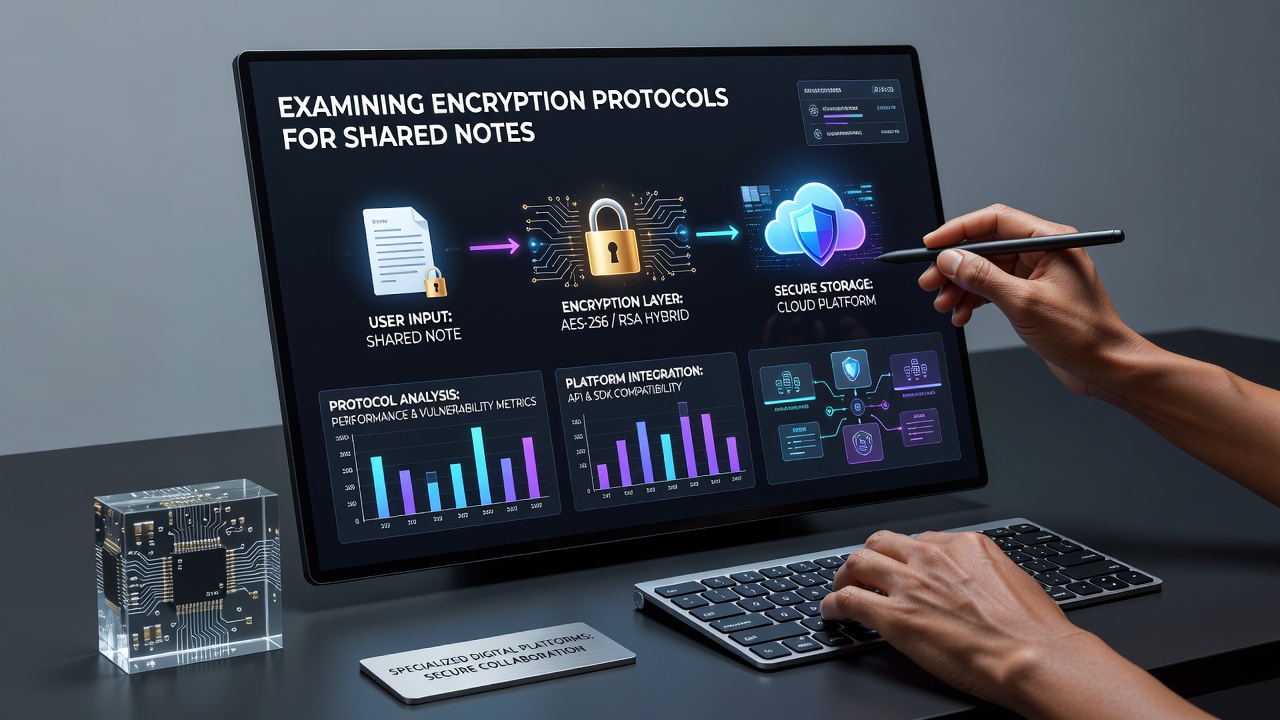
As of October 2026 updates to post-quantum resistant algorithms begin appearing in pilot programs at several academic and corporate note platforms where lattice-based schemes supplement existing RSA structures to prepare for future threats from quantum computing advances.
Platform-Specific Adaptations
Enterprise note systems integrate homomorphic encryption techniques in limited scopes to allow search operations on encrypted indexes without full decryption and this permits users to locate content across shared repositories while the underlying data stays protected at rest, and reports from the Australian Cyber Security Centre highlight how such adaptations meet compliance requirements in regulated sectors like healthcare and legal services.
Real-time collaboration features depend on secure multiparty computation protocols that reconcile edits from different users without revealing intermediate states and testing data reveals these methods maintain consistency rates above 99 percent in high-concurrency environments when combined with conflict-resolution algorithms that operate on ciphertext.
Security Audits and Standards Compliance
Independent audits conducted by third-party firms verify that encryption implementations match published specifications and any deviations trigger remediation within defined timelines while regulatory frameworks in teh European Union require documentation of cryptographic choices under data protection rules and similar expectations appear in Canadian federal guidelines for digital record handling.
Case examples include platforms that adopted hybrid encryption stacks after identifying weaknesses in older CBC modes and migrated to authenticated encryption with associated data constructions like AES-GCM which eliminate padding oracle risks during shared note synchronization.
Conclusion
Encryption protocols continue to evolve in response to emerging computational threats and regulatory demands so specialized platforms maintain ongoing development cycles that incorporate new standards as they achieve maturity and widespread validation from the cryptographic community.